As cyber-attacks become more and more common, protecting your personal data is becoming increasingly difficult. There are so many ways one could access one of your accounts. If you use that account to login into your social media, you are doomed. Why? Because nearly all known password reset links are sent via email. If a malicious individual has full access to that email, they can use it to reset passwords on all the accounts. Hence, you will be locked out of your email and all the accounts, as mentioned earlier.
Two-factor authentication (2FA) is a login check that asks for two different kinds of proof before it lets you in. Usually that's your password plus something you physically have, like a code from your phone or a hardware key. If someone steals your password, they still can't get in without the second factor. If you're new to this space, our guide on securing yourself online covers the broader basics before you go deeper.
We know this doesn't sound very comforting, so some measures can help prevent this catastrophe from happening. One such measure is two-factor authentication which we will talk about today. In this guide, we will explain everything about two-factor authentication and how you can use it in your system. But not every 2FA method gives you the same protection, and once you know which ones are weaker, you'll know which to pick.
🔐 What Is Two-Factor Authentication (2FA)?
Two-factor authentication adds an extra security level when you log into a website, online bank account, credit card portal, or any other site. Almost any website with a system with users will have single-factor authentication with a username and a password. Sometimes, however, even the strongest of passwords are not enough to keep an important account secure.
2FA is a type of multi-factor authentication (MFA) that uses exactly two factors, and they have to come from different categories. Two common examples are a password plus a six-digit code from Google Authenticator, or a password plus a tap on a YubiKey. As can be guessed from the name, it requires one extra step to log into a website or access an online account. First, you will have to enter the username and password to get to the second step. Then the site will, in most cases, send you a text message or email with a verification code that you will have to enter into the site to get access to the account.
Why does this matter? Passwords get reused, phished and leaked in data breaches every day. According to the FBI's figures, reported online scam losses reached $16.6 billion in 2024. Account takeover is part of that total.
⚙️ How Does 2FA Work?
Understanding the inner workings of Two Factor Authentication (2FA) is crucial to appreciating its effectiveness in safeguarding your online presence. Authentication is the process of confirming a user's identity. In this context, authentication revolves around the notion of "factors," which are the elements used to verify who you are. So if you're wondering what is 2FA code, these factors serve as the building blocks of 2FA. Every authentication factor falls into one of three categories:
- Something you know (Knowledge Factor): a password, PIN or passphrase. This factor pertains to something the user knows. It typically involves information that only the user should possess, such as a password, PIN, or a specific piece of knowledge.
- Something you have (Possession Factor): a phone, an authenticator app, a security key. Possession factors involve something the user has in their physical possession, like a security token, a mobile device, a smart card, or even an authentication app.
- Something you are (Inherence Factor): a fingerprint or a face scan. Inherence factors are characteristics inherent to the user's physical self. These include biometric traits such as fingerprints, facial recognition, voice patterns, and even behavioral biometrics like keystroke dynamics or gait.
Step-by-Step Process of 2FA Verification
Here's what a typical login looks like. You type your email and password into your hosting dashboard. The server checks the password and then asks for a one-time password (OTP). You open Microsoft Authenticator, read the 30-second TOTP code and enter it. If both checks pass, you're in.
- User Initiation: The process typically begins when a user attempts to log in to a website or application that requires 2FA. They enter their username and, in most cases, their password as the first factor, the knowledge factor.
- Factor 1 (Knowledge Factor): The system validates the user's identity by checking the first factor, typically a password. If the entered credentials match the stored data, the system proceeds to the next step.
- Factor 2 (Possession or Inherence Factor): Here comes the crucial second factor, which falls into either the possession or inherence category. The user is prompted to provide this factor, which could be in the form of a security token, a smart card, a mobile app to generate a one-time code, or biometric data such as a fingerprint scan or facial recognition.
- Authentication Confirmation: Upon successful validation of the second factor, the user is authenticated and granted access to the website or application. The presence of two factors ensures a significantly higher level of security, making it challenging for malicious actors to gain unauthorized access.
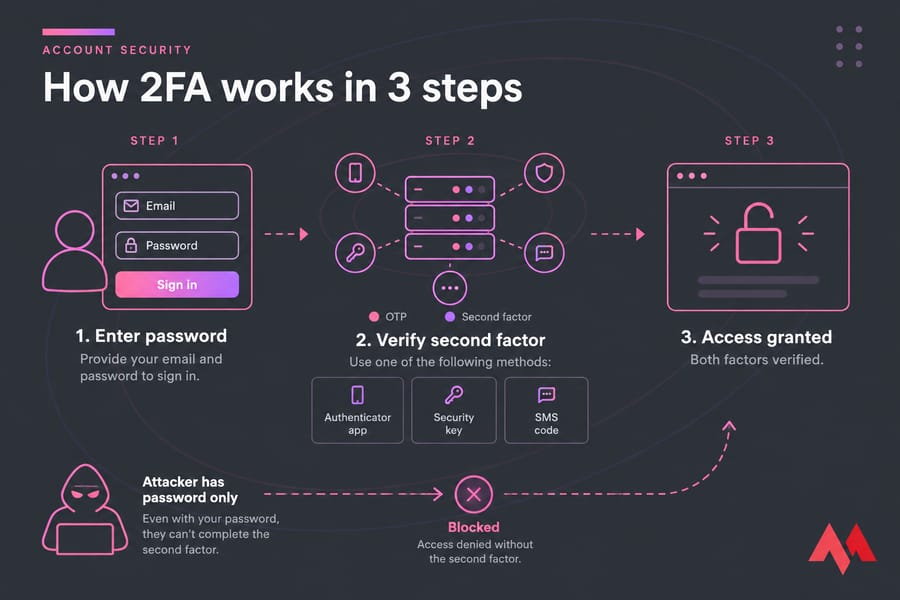
With single-factor authentication, one stolen password is enough to get in. With 2FA, an attacker has to steal two unrelated things. That's a much bigger job.
🔀 2FA vs MFA vs Two-Step Verification
MFA means two or more factors. 2FA is the version that uses exactly two, so every 2FA setup counts as MFA, but not every MFA setup is 2FA.
"Two-step verification" is looser. Google and other companies use the term because the second step isn't always a different factor category. Two steps that both rely on something you know, like a password followed by a security question, don't count as true 2FA.
🛡️ How Does Two-Factor Authentication Help?
Aside from the methods of attack mentioned previously, there are still countless ways to gain access to your accounts. Two-factor authentication adds an extra step of security to prevent a malicious individual who has gotten access to your password from being able to log in to the account.
What Threats Are Out There?
Before getting into preventative measures, we need to identify what exactly we should care about. Even if you have a very strong password, there are ways hackers could get access to your accounts without even ever having it through things like phishing scams and installing keyloggers on your machine.
Cracking Weak Passwords with Brute Force Attacks
If your password is just a word followed by some numbers, especially if it is not very long, hackers can brute force it. What does that mean? They run a script that attempts every single combination of characters and numbers until they get it right. If you're unsure how to build credentials that survive this, our guide on how to choose a secure password walks through the fundamentals.
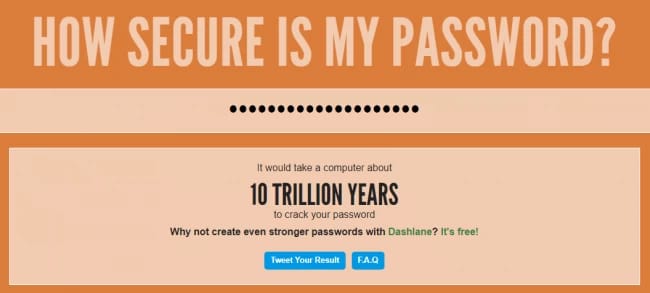
There is a way to test whether your password is susceptible to this style of attack with tools such as HOW SECURE IS MY PASSWORD?, which will tell you approximately how long it would take a computer to crack your password.
Please note that you should not enter your same password into these tools, but one of similar characters and format. For example, if your password is 777monovm@Pa55, then enter 936tokern#Rk67. As you can see, they are completely different to our eyes, but to a computer that is trying to crack it, they would be about the same since they consist of the same character types in the same positions.
Dictionary Attacks
Whenever you read any suggestions for creating a strong password, they always mention not including any words within a dictionary. This is because hackers can run scripts that enter every word in the dictionary and even try different combinations of said words. Therefore if your password is catsarecute, such an attack would crack it within minutes.
Keyloggers
This is one nasty virus that you can catch while browsing the web. It simply runs in the background upon startup, records every keypress that you do, and shares it with the attacker. Not only are your passwords in danger, but your entire private conversations.
Phishing Scams
These attacks are a bit different from the rest, they do not actually install any malware or run any malicious scripts. These are sites on the internet that are nearly identical to legitimate popular sites such as Facebook and Twitter. Once you try to log in, however, they do nothing and send the login information you used to the attackers' database.
🧩 Common Types of 2FA Methods
Two-factor authentication offers a variety of methods to strengthen your online security. Each method adds an additional layer of protection to verify your identity. You'll run into six main options. Some are much stronger than others:
- SMS codes: A code arrives by text message. It's easy to use and works on any phone, but texts can be intercepted or redirected. Use it only when nothing better is offered.
- Authenticator apps: Google Authenticator, Microsoft Authenticator and Authy generate TOTP codes on your device, and they work offline. This is a solid default for most accounts.
- Push notifications: You tap "Approve" on your phone. It's convenient, but it's open to approval spam (covered below).
- Biometrics: Face ID or a fingerprint. In most setups, biometrics just unlock something you already have, such as your phone or a passkey. They rarely act as a standalone factor over the network.
- Security keys: Physical FIDO2 devices like a YubiKey. They're the strongest option for high-value accounts.
- Passkeys: Cryptographic credentials stored on your devices, built on FIDO2/WebAuthn. They can replace the password entirely.
SMS-Based Authentication
SMS-based 2FA, also known as text message authentication, is one of the most common and user-friendly methods. It relies on your mobile phone for verification. When you enable SMS-based 2FA, you link your mobile phone number to your account. After entering your username and password, the system sends a one-time verification code to your mobile device via SMS. You receive the code and enter it into the login screen. If the code matches, you gain access to your account. It's easy to set up and use, with no need for additional apps or hardware, but it is vulnerable to SIM card hijacking and interception.
Authenticator Apps
Authenticator apps offer more secure and convenient examples of 2 Factors method. Popular apps like Google Authenticator, Authy, and Microsoft Authenticator generate time-based one-time passwords (TOTPs). You download and install your chosen authenticator app, add your accounts by scanning QR codes or entering setup keys, and the app generates a new code every few seconds. When logging in, you enter the current code displayed in the app. This offers increased security compared to SMS-based 2FA and works offline, but requires installation of a separate app, and backup options are essential in case of device loss.
Biometric Authentication
Biometric authentication leverages unique physical characteristics to verify your identity. Common biometric factors include fingerprint recognition, facial recognition, iris or retina scanning, and voice recognition. This is highly secure, as biometric data is difficult to replicate, and convenient and user-friendly. However, it requires compatible hardware and raises possible privacy concerns regarding biometric data storage.
Hardware Tokens and Security Keys
Hardware tokens and security keys offer the highest level of security but require physical devices. Hardware tokens are small, physical devices that generate one-time passwords that you enter during login. Security keys are USB or NFC devices that provide cryptographic proof of your identity. These are exceptionally secure and resistant to hacking, ideal for high-security environments, but costly and not as user-friendly for everyday use, with a risk of losing the physical token.
Choosing the right 2FA method depends on your security needs and preferences. SMS-based authentication and authenticator apps are suitable for most users, while biometric methods and hardware tokens are ideal for those requiring the highest level of protection.
🏆 Which 2FA Method Is Most Secure?
Here's the practical ranking, from strongest to weakest:
| Method | Security level | Phishing-resistant? | Works offline | Best for |
| Security key / passkey | Highest | Yes | Yes | Admin, email, cloud, registrars |
| Authenticator app (TOTP) | High | No | Yes | Most personal and work accounts |
| Push notification | Medium–High | No | No | Corporate SSO with number matching |
| SMS code | Low–Medium | No | No | Fallback only |
| Email code | Low | No | No | Last-resort fallback |
To be clear, SMS is still far better than no 2FA at all. But NIST SP 800-63B states plainly that OTP authentication isn't phishing-resistant. That covers any method where you type a code by hand, because a convincing fake site can ask you for the code and pass it along to the real one. CISA's MFA guidance ranks physical security keys as the most secure option.
🚨 Can 2FA Be Hacked or Bypassed?
Yes. 2FA cuts your risk dramatically, but it doesn't make an account impossible to break into. These are the four attacks I see most often:
SIM swapping
An attacker talks your mobile carrier into moving your number to their SIM card. From then on, your SMS codes go to them. This is the main reason SMS sits near the bottom of the ranking.
MFA fatigue and push bombing
The attacker already has your password, so they keep triggering push prompts until you tap "Approve" just to make them stop. Number matching helps, where you have to type a number shown on the login screen. The simplest defense is never approving a login you didn't start yourself.
Real-time phishing proxies
Tools like Evilginx sit between you and the real site. They relay your password and OTP as you type them, so the attacker is logged in within seconds.
Session cookie and token theft
Once you've logged in, infostealer malware can grab your session cookie and replay it, which skips 2FA completely. The fix here is keeping your devices clean and setting short session lifetimes. A better second factor won't help.
🎣 What Is Phishing-Resistant MFA?
Phishing-resistant MFA ties your login to the real website's domain using public-key cryptography. There's no code to type, so there's nothing for a fake site to capture. A security key registered for yourhost.com won't answer a request from yourh0st.com.
FIDO2/WebAuthn security keys and passkeys work this way. NIST's guidance now includes syncable authenticators like passkeys. Adoption has also moved beyond early adopters: the FIDO Alliance estimated in May 2026 that 5 billion passkeys were in use worldwide.
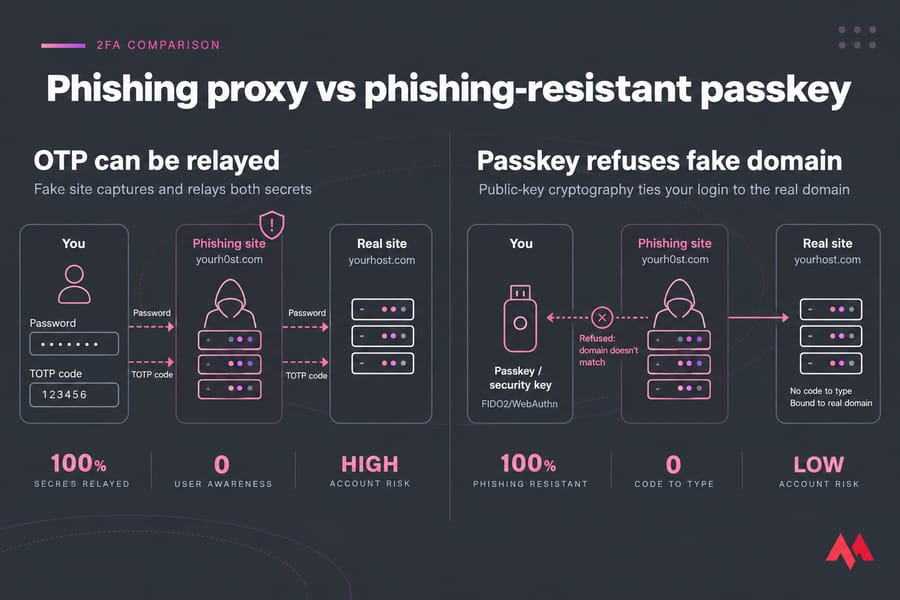
So do passkeys replace 2FA? In a sense, yes. A passkey already combines something you have (the device) with something you are or know (your biometric or PIN) in a single step. It gives you MFA-level protection without a password.
🛠️ Implementing Two-Factor Authentication
Enabling Two-Factor Authentication (2FA) is a powerful step toward enhancing your online security. In this section, we'll explore how to implement 2FA across various online services, provide step-by-step guides for setting it up, and highlight best practices for managing and securing your 2FA credentials.
Enabling 2FA for Popular Online Services
Email Services:
- Gmail: Google offers robust 2FA options. Navigate to your Google Account settings, click on "Security," and follow the prompts under "2-Step Verification."
- Outlook: Microsoft provides 2FA through its Authenticator app or SMS. Enable it in your Outlook account settings.
Social Media:
- Facebook: Access your Facebook Security Settings and click on "Use two-factor authentication" to set it up using an authentication app or your phone number.
- Twitter: Visit your Twitter account's "Security and account access" settings to enable 2FA using an authentication app or SMS.
Banking and Financial Services:
- Online Banking: Many banks now offer 2FA. Contact your bank's customer service or visit their website for guidance on enabling it.
- Payment Apps: Services like PayPal and Venmo offer 2FA options in their security settings. If you trade currencies, the same discipline applies — see our guide on securing Forex trading accounts for the financial-specific angle.
Self-Hosted Platforms:
If you run WordPress, protecting /wp-admin is its own project — setting a password for wp-admin adds server-level authentication on top of your CMS login, which pairs well with 2FA on the WordPress user account itself.
Step-by-Step Guides for Setting Up 2FA on Different Platforms
Mobile Apps:
- Google Authenticator: Install the app on your smartphone, add an account by scanning a QR code or entering a setup key. The app generates time-based one-time passwords (TOTPs) for 2FA.
- Authy: Install Authy from your app store, create an account or sign in, and follow the app's instructions to add accounts and enable 2FA.
Social Media Platforms (Using Facebook as an Example):
- Log in to your Facebook account.
- Navigate to "Settings & Privacy" > "Settings."
- Click on "Security and Login."
- Scroll down to "Two-Factor Authentication" and click "Use two-factor authentication."
- Choose between an authentication app or text message (SMS) as your 2FA method.
- Follow the on-screen instructions to complete the setup.
How to Set Up 2FA Safely
Secure your accounts in this order:
- Primary email. Password resets for everything else go through it.
- Password manager. It holds all your other logins.
- Banking and payment accounts.
- Cloud, hosting, domain and admin accounts.
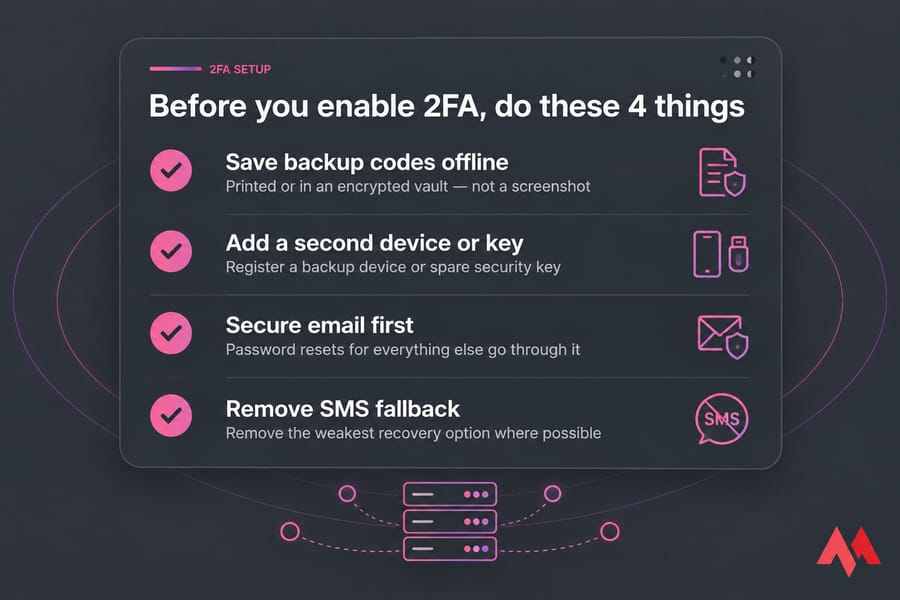
On every account, pick the strongest method it offers. Remove SMS as a fallback where you can, because attackers will target the weakest option you leave enabled. Save your backup codes as soon as they're shown, either printed or in an encrypted vault. Don't keep them as a screenshot in your camera roll.
Best Practices for Managing and Securing 2FA Credentials
- Use a Password Manager: A password manager helps you keep track of your 2FA codes and passwords securely. Popular options include LastPass, 1Password, and Bitwarden.
- Backup Codes: Some services offer backup codes when you set up 2FA. Keep these in a secure location. They can be used to regain access if you lose your 2FA device.
- Secure Your Devices: Ensure that the devices you use for 2FA, such as smartphones, are adequately protected with PINs, fingerprints, or facial recognition.
- Keep 2FA Codes Secure: Avoid taking screenshots or photos of 2FA QR codes or backup codes. Store them in a secure, offline location.
- Avoid Using SMS: While SMS-based 2FA is better than no 2FA, it's less secure than app-based 2FA. Whenever possible, opt for app-generated codes.
🔑 What Happens If You Lose Your 2FA Device?
You can get back in, but only if you prepared ahead of time. Before you lose anything, store your recovery codes offline in a place you'll actually remember, register a second security key or a backup device, and use an authenticator with encrypted backup or add the same account to two apps.
If your phone is stolen, sign in with a recovery code, revoke the lost device in your security settings, sign out all active sessions and re-enroll a new authenticator. If you have no codes at all, you'll have to go through the provider's identity verification. That can take days, which is exactly why the preparation matters.
🏢 2FA Best Practices for Businesses and Admin Accounts
For anyone running infrastructure, this is where 2FA matters most. A single compromised admin login can expose every site, database and customer you host. If you're securing a server, a solid baseline of VPS security tips pairs well with 2FA on the control panel side, and if you manage Windows desktops or servers over Remote Desktop, the same logic applies — see our guide on enhancing RDP with multi-factor authentication. Turn on 2FA, ideally with hardware keys, for:
- VPS and cloud provider dashboards
- Hosting control panels like cPanel, Plesk and DirectAdmin
- Domain registrars and DNS providers, since a hijacked DNS record can redirect everything
- Email admin consoles
- GitHub, GitLab and CI/CD tools
- Remote access through VPN, RDP gateways and SSH bastions
For privileged accounts, use phishing-resistant MFA. TOTP is fine for everyday users, but admins are exactly who phishing proxies target. Issue each admin two FIDO2 keys, one for daily use and one locked away as a spare, and audit enrolled authenticators every quarter. And because brute-force traffic is often just the first layer of an attack, hosting the workloads behind your admin panel on a DDoS-protected VPS removes a whole category of noise before it ever reaches your login page. If the site behind that login is public-facing, our broader guide on securing your website covers the other layers you'll need.
🔬 Why Is Two-Factor Authentication Important?
Passwords have been the mainstream form of authentication since the start of the digital revolution. But this security measure is far from infallible. Here are some worrying facts about this traditional security measure:
- 90% of passwords can be cracked in less than six hours.
- Two-thirds of people use the same password everywhere.
- Sophisticated cyber attackers have the power to test billions of passwords every second.
The vulnerability of passwords is the main reason for requiring and using 2FA. Two-factor authentication might seem like a hassle. After all, you'll need to take an extra step to log onto your favorite websites. Without 2FA, you could be leaving yourself vulnerable to cybercriminals who want to steal your identification, access your bank accounts, or hack into your online credit card portals. Without a complex, unique password for each of your online accounts, a skilled hacker may be able to crack your passwords. And once they do, they can easily access the personal and financial information in any accounts with that username and password combination.
✨ Benefits of Two-Factor Authentication
2 factor authentication (2FA) offers a multitude of advantages, enhancing online security and safeguarding sensitive information.
Enhanced Security
2FA provides an additional layer of defense, bolstering protection against unauthorized access. Even if a password is compromised, the second factor serves as a formidable barrier, preventing malicious actors from gaining entry.
Mitigation of Password Vulnerabilities
2FA mitigates password-related vulnerabilities that often plague online security. It combats issues like password reuse and brute-force attacks, reducing the risk of unauthorized access.
Safeguarding Data Privacy
By fortifying authentication processes, 2FA safeguards sensitive information and preserves data privacy. It ensures that only authorized individuals can access confidential data, bolstering privacy and compliance measures.
🧬 Biometrics Two-Factor Authentication
One of the major issues with passwords and tokens is that they can't prove your identity. Biometrics solves that problem. Adding biometrics as an authentication factor is the best way to prove identity because your biometrics are you. Identity-based access control is a significant improvement over alternative authentication factors because you can't forget it, you can't lose it, and they are extremely difficult to steal and unique to you.
Biometrics are light years more secure than other authentication factors and make accessing sensitive information and remote servers easy and effective. When you utilize smartphones to deploy biometric authentication, it's easy and effective; people who complain about 2FA being a nuisance won't have anything to complain about anymore.
To make one final point, many consumers are concerned about protecting their biometrics. This is a valid concern, but if the biometrics are properly implemented, it will enhance personal and professional privacy. Using visual cryptography techniques and a distributed data model helps make sure your biometrics and sensitive information will never end up in the wrong hands. This way, you can use 2FA solutions and still sleep at night knowing your biometrics and data are safe.
⚠️ Challenges and Considerations
While Two-Factor Authentication (2FA) is a formidable defense against cyber threats, it is not without its challenges and considerations. In this section, we explore the potential vulnerabilities and risks associated with 2FA, the delicate balance between security and user experience, and the importance of backup and recovery options.
Potential Vulnerabilities and Risks
While 2FA boosts security, it's not foolproof. The second factor, like a mobile device, can be stolen or exploited. Phishing attacks can trick users into revealing both factors, and provider breaches may expose user data.
Balancing Security and Convenience
Finding the right balance between security and user experience is crucial. Complex 2FA can deter users, so user-friendly methods and education are key. Offering diverse authentication options empowers users to choose what suits them.
Backup and Recovery
Planning for device loss or failure is essential. Backup codes and alternative contact methods prevent lockout, ensuring users can access their accounts. Striking a balance between security and user-friendly recovery options is vital.
🚀 Future Trends in Two-Factor Authentication
As the digital landscape evolves, so does the realm of Two-Factor Authentication (2FA). The future promises exciting advancements that will further bolster online security. Let's explore the emerging trends and the integration of 2FA with other cutting-edge security measures.
Emerging Technologies in Authentication
1. Passwordless Authentication:
Passwords have long been a weak link in online security due to their vulnerability to breaches and human error. Passwordless authentication methods aim to eliminate the need for traditional passwords altogether. Some emerging passwordless methods include:
- Biometric Authentication: Leveraging biometric data like fingerprints, facial recognition, and iris scans for seamless, secure authentication.
- FIDO (Fast Identity Online): FIDO standards enable passwordless authentication using hardware tokens or biometrics.
2. Biometric Advancements:
Biometrics continues to evolve, offering enhanced accuracy and security. Future biometric advancements may include:
- Behavioral Biometrics: Analyzing user behavior, such as typing patterns, mouse movements, and voice recognition, for continuous authentication.
- Heartbeat Authentication: Utilizing the unique patterns of an individual's heartbeat as a biometric identifier.
Integration of 2FA with Other Security Measures
1. Multi-Factor Authentication (MFA):
While 2FA is a powerful security measure, MFA takes it a step further by incorporating additional factors beyond the initial two. This can include something the user is, knows, and has, making it even more challenging for attackers to breach security.
2. Adaptive Authentication:
Adaptive authentication is a dynamic approach that assesses the risk of a login attempt in real-time and adapts security measures accordingly. It evaluates various factors, such as the user's location, device, behavior, and threat intelligence, to determine the appropriate level of authentication required. This ensures that strong authentication is reserved for high-risk scenarios while allowing smoother access for routine activities.
3. Blockchain-Based Authentication:
Blockchain technology is gaining attention as a secure means of authentication. Decentralized identity and self-sovereign identity solutions leverage blockchain to provide users with control over their identity data, enhancing privacy and security.
4. Zero Trust Security:
The Zero Trust model assumes that no user or device is inherently trustworthy, even if they are within the corporate network. Zero Trust security integrates continuous authentication and strict access controls, making it a powerful complement to 2FA.
5. IoT Authentication:
With the proliferation of Internet of Things (IoT) devices, securing them becomes paramount. Integrating 2FA and other advanced authentication methods into IoT ecosystems ensures that these devices remain secure against unauthorized access.
🎯 Conclusion
Having two-factor authentication on your accounts is still not the end-all solution to protecting your online accounts. Along with 2FA, you should also have strong passwords for all your accounts and use a different password for each one. For ease of use, we recommend using a password manager that will help you keep track of all of them. If you need inspiration for building memorable yet strong credentials, our list of secure password ideas is a good starting point.
We know you have surely heard this before, but we will stress the importance of this statement again: have your password be at least 12 characters long and include both uppercase & lowercase letters along with numbers and special characters (such as &, #, $, etc.); do not include any dictionary words or personal information within the passwords such as birthdate, name, etc. Keeping your computer malware-free is also crucial to your online accounts' security as even certain types of 2FA can be deciphered with a keylogger. For instance, if the only type of two-factor authentication you have on one of your accounts is a security question, the keylogger will record the answer as well.
Turn on 2FA today, starting with your email and admin accounts. Use an authenticator app as your baseline, and move to passkeys or security keys wherever the service supports them. Save your backup codes before you need them.